The customer is a multi-entity financial-services group in India. Its licensed subsidiaries are regulated by SEBI, IRDAI and AMFI for stock broking, investment advisory, portfolio management, insurance broking and fund distribution. Its digital platforms, including a customer-facing web application, data pipelines and security tooling, ran on Microsoft Azure across roughly 26 virtual machines and 14 virtual networks.
Aivar Innovations partnered with the customer to migrate the estate from Azure to AWS and to build a governed, multi-account network foundation. Each regulated entity has its own compliance boundary, and production and disaster recovery are anchored in India.
Project Start Date: Apr 16 2026
Project End Date: Aug 01 2026

The existing network could not support a safe migration or the segregation that regulators require. Key challenges included:
Without a reliable, encrypted path between the two clouds, the database could not be replicated and applications could not be moved in stages. The estate's Azure Advisor security score was 21 out of 100. Continuing as-is left the customer exposed to regulatory findings and to outages from a single gateway.
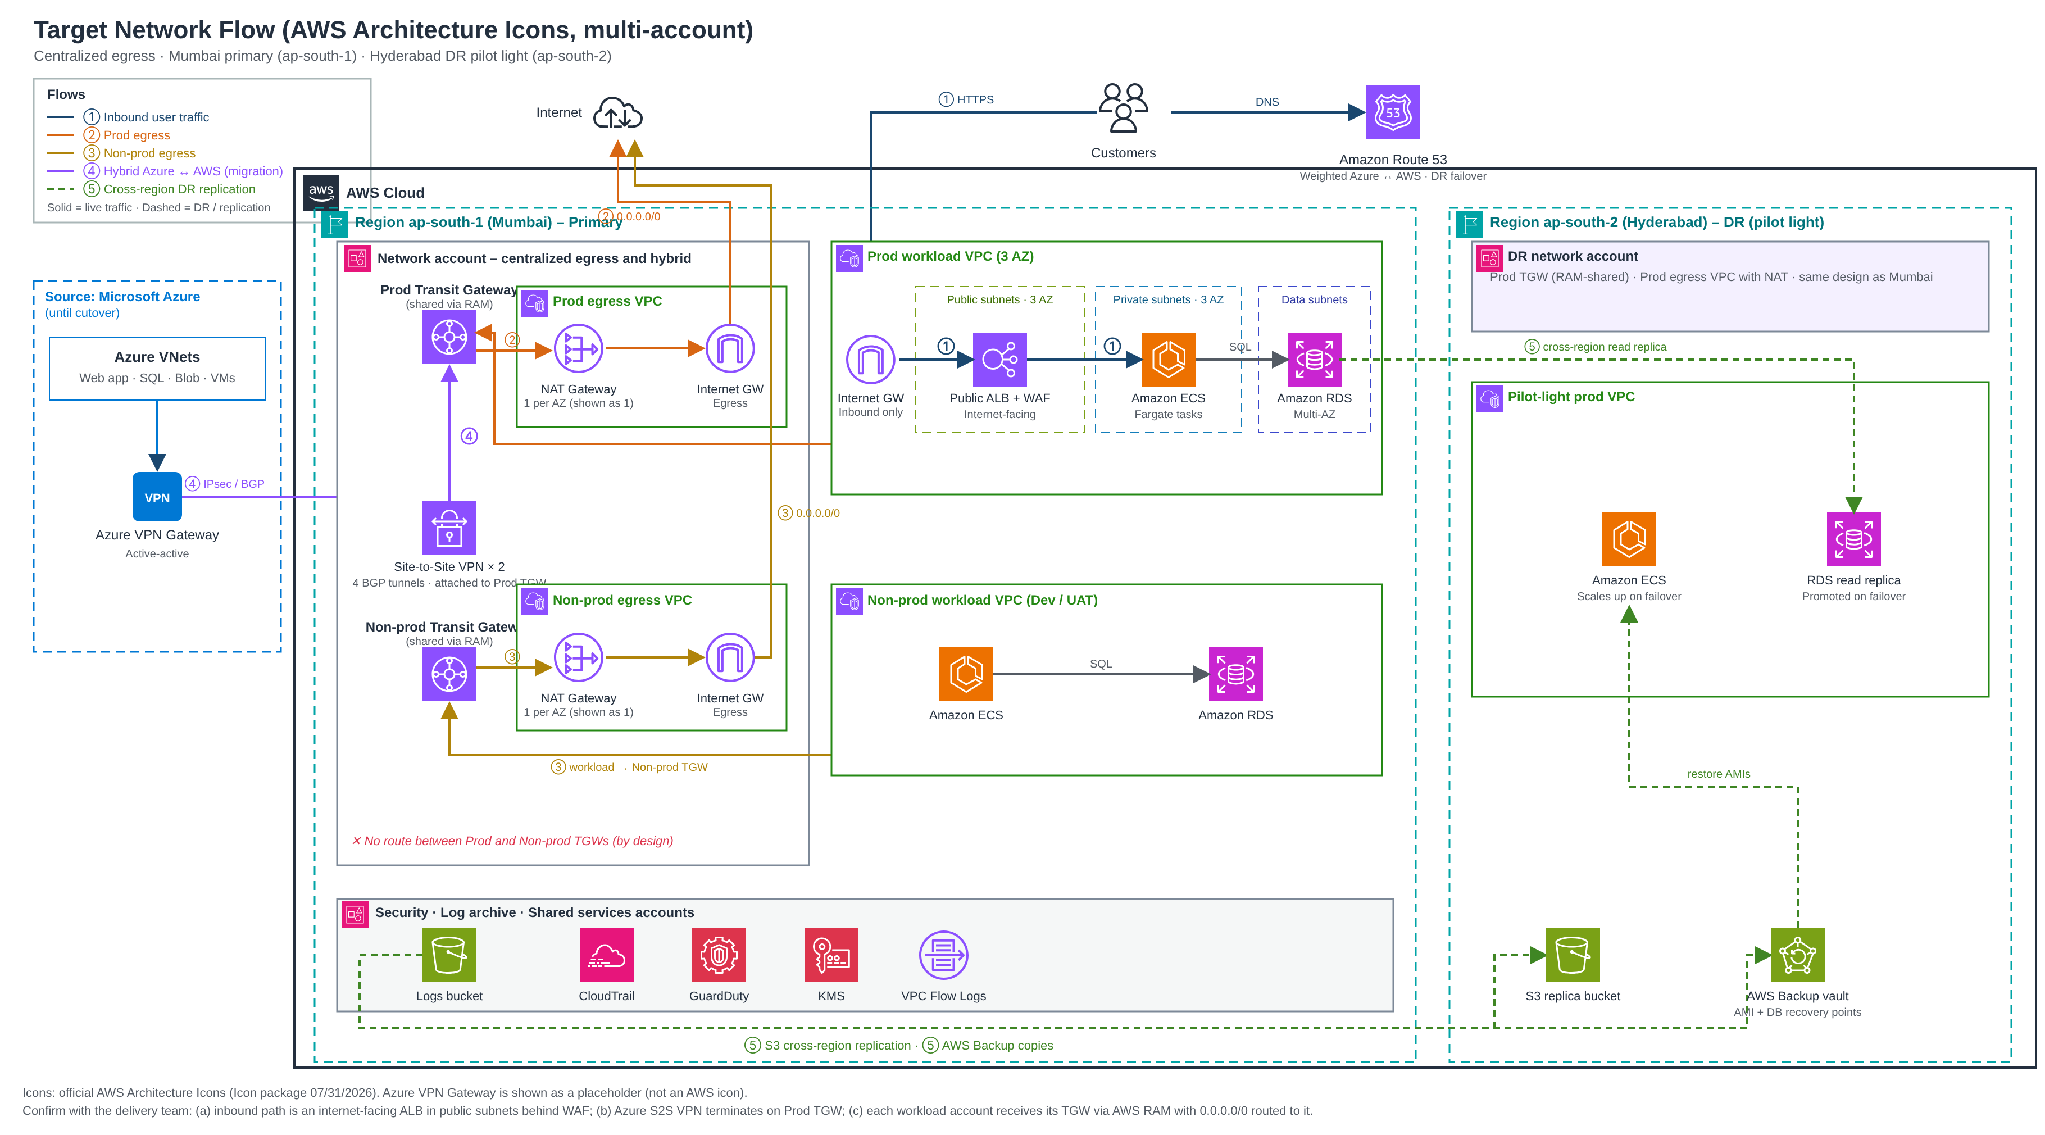
Aivar designed and delivered a network foundation in Mumbai (ap-south-1), with disaster recovery in Hyderabad (ap-south-2). The solution combined the following, delivered as Terraform code:
Alternatives were weighed against regulatory and migration constraints. A shared Transit Gateway was rejected because it makes cross-domain routes the default. The per-domain design costs more gateways, egress VPCs and KMS keys, and the customer accepted that cost. Application-layer failover was chosen over DNS-based egress failover, which was judged too slow and too opaque.
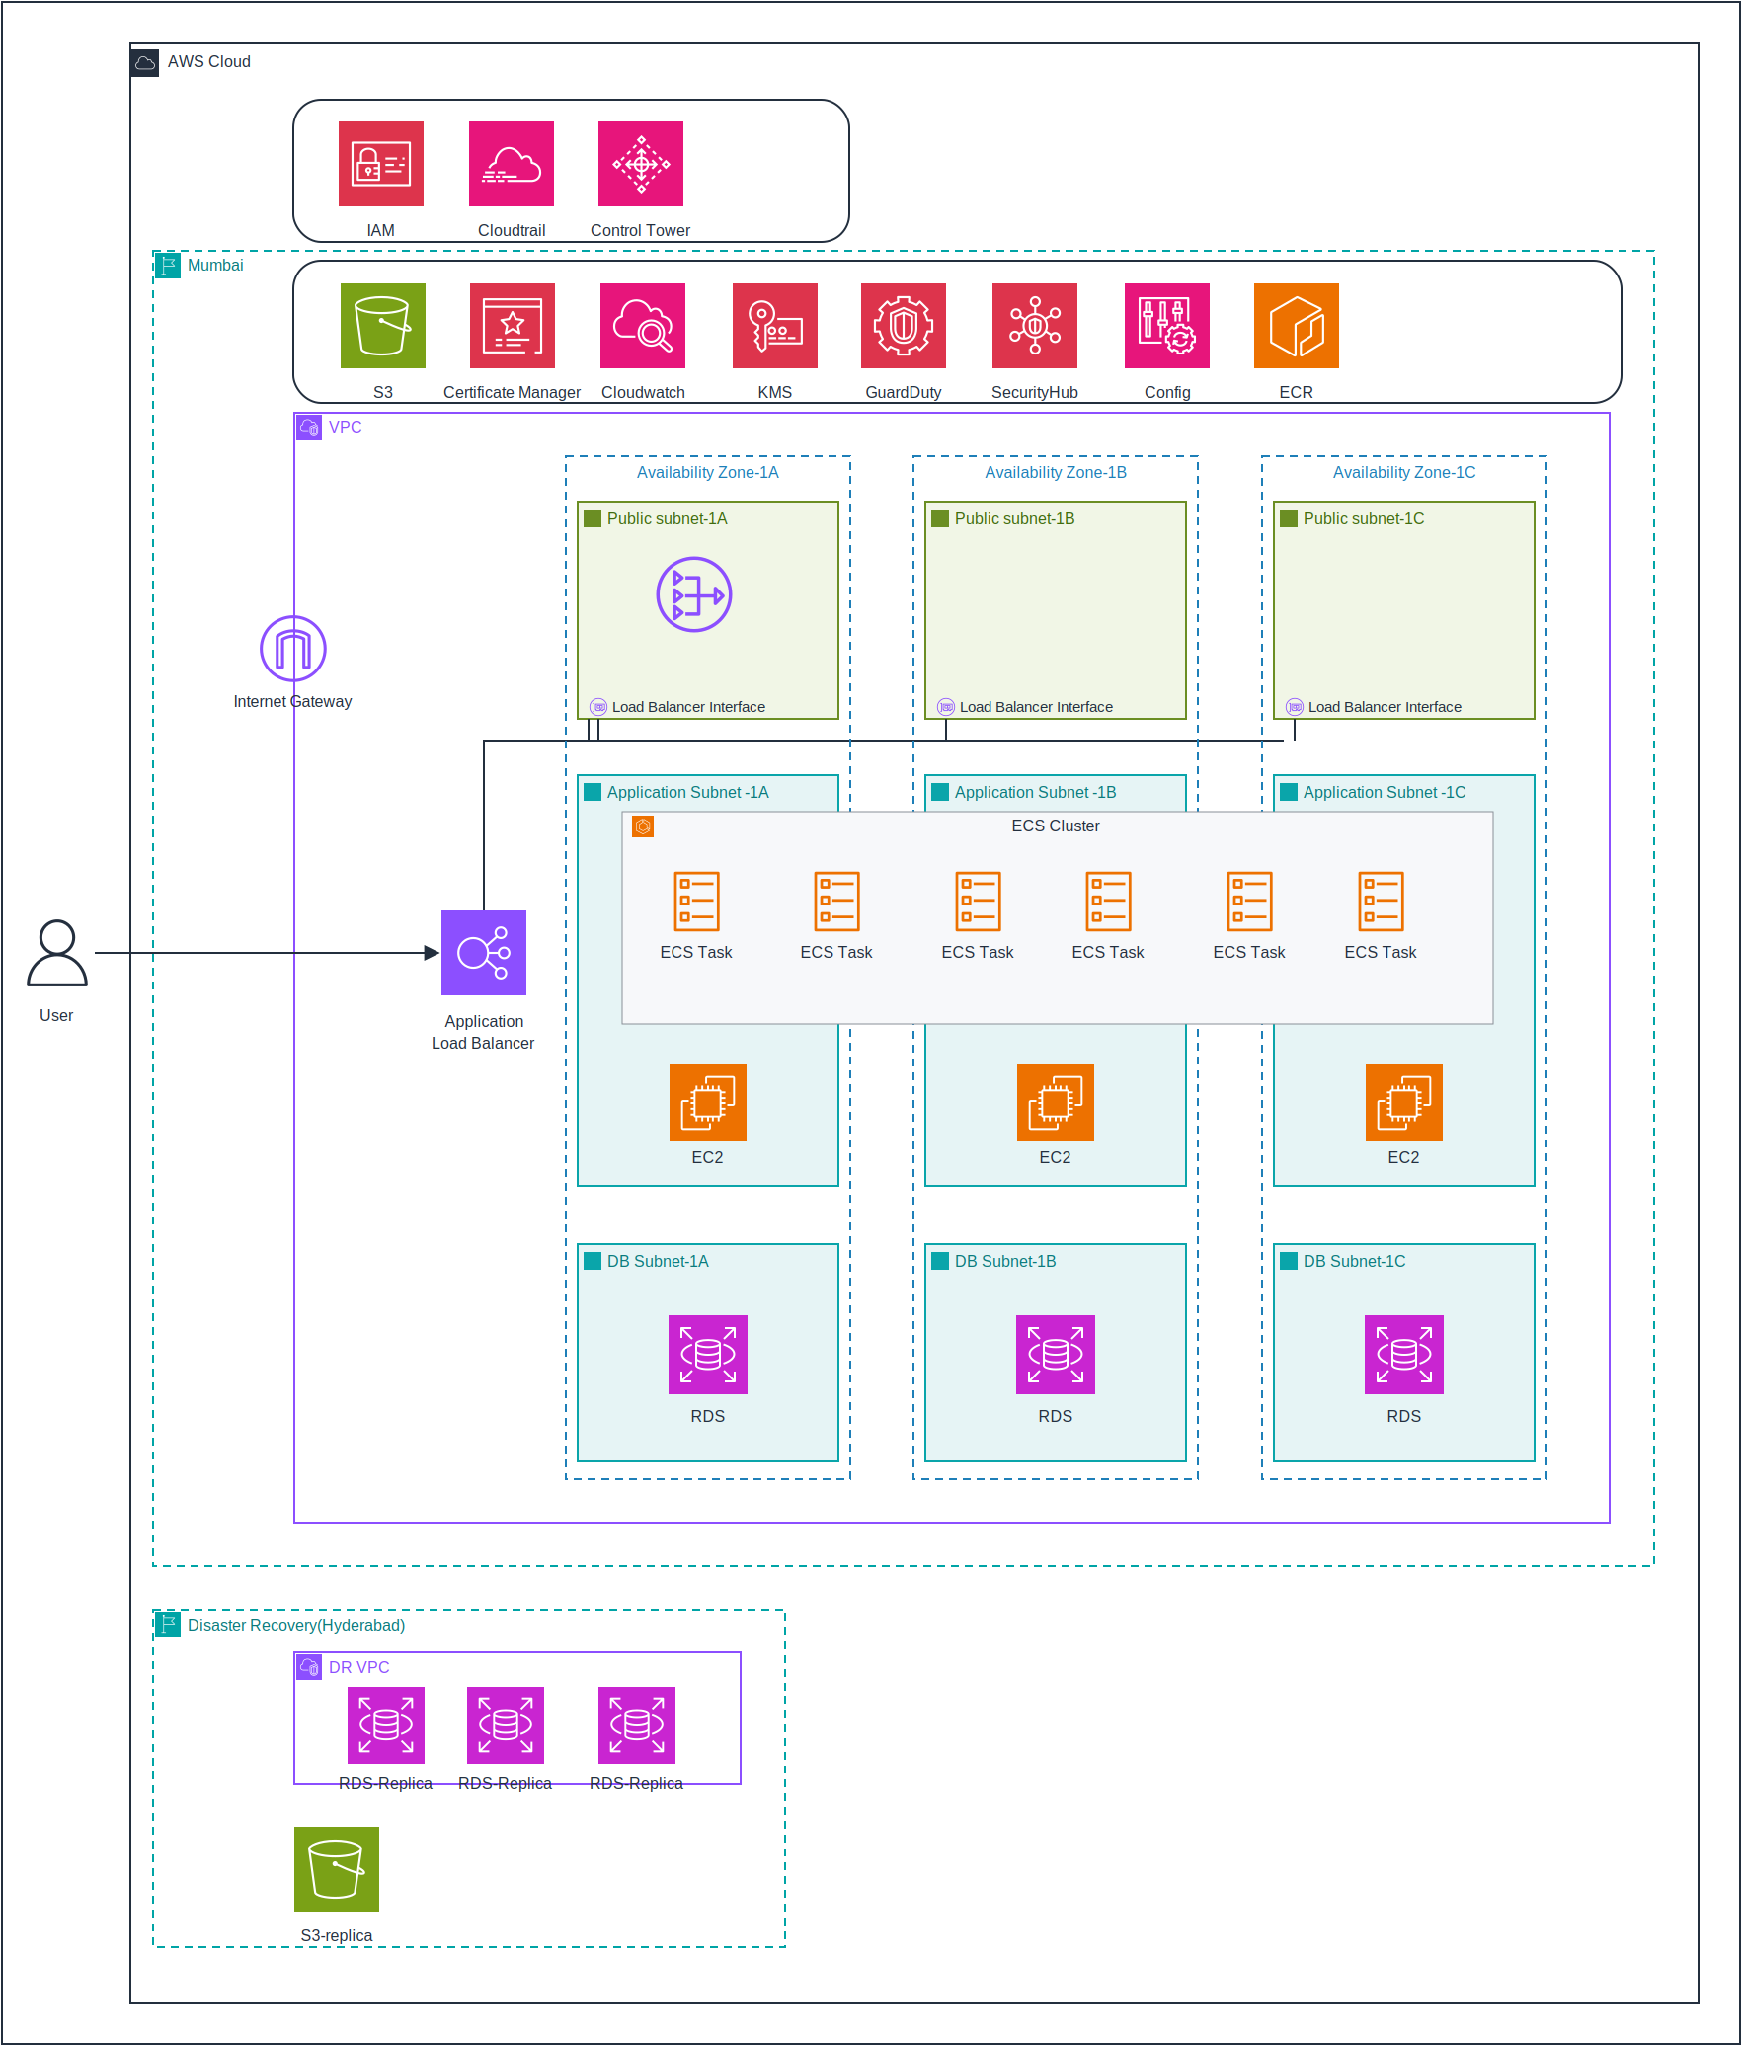
The architecture spans two regions. In the primary region, the application runs as an Amazon ECS cluster across three Availability Zones, behind an Application Load Balancer. Each Availability Zone has a database subnet holding an Amazon RDS instance. Shared services, including IAM, CloudTrail, Control Tower, KMS, GuardDuty, Security Hub, AWS Config, CloudWatch and ECR, support the VPC. The disaster-recovery VPC in Hyderabad holds three RDS cross-region read replicas, an S3 replica bucket, and AWS Backup copies of AMIs and database recovery points for restore during failover.