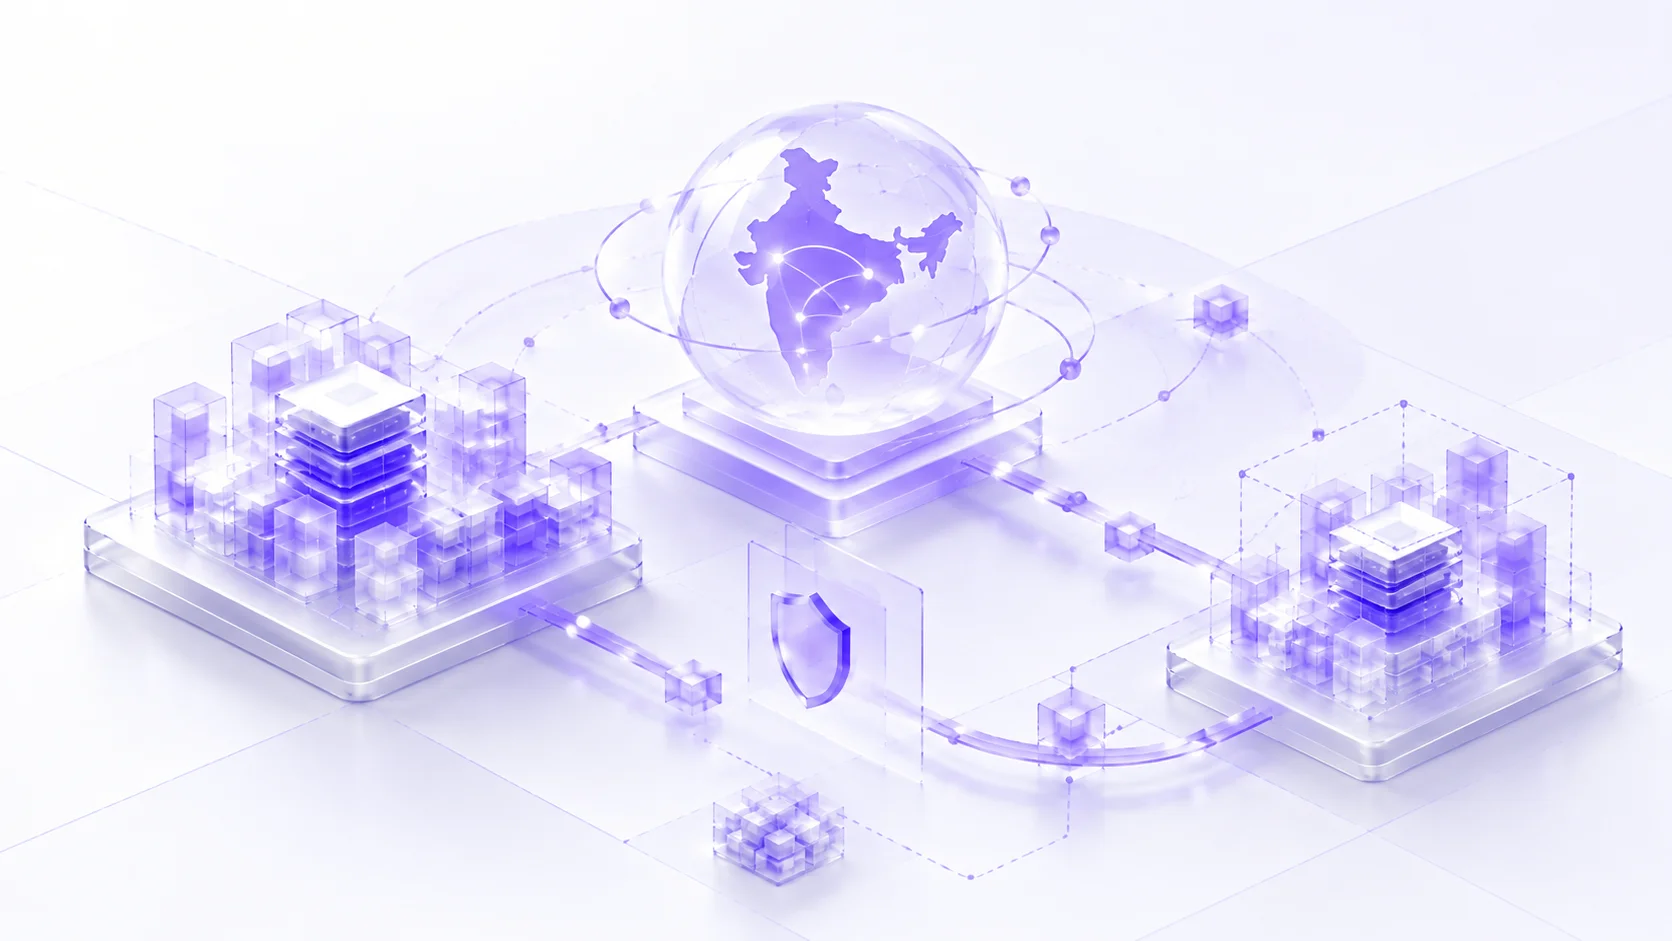
The customer is a cloud-native technology company serving the SMB/mid-market segment with a customer-facing production application. Aivar Innovations designed and delivered a multi-Region architecture on Amazon Web Services (AWS) with defined trust boundaries, layered security controls, identity-based access management, and policy-enforcement points, migrating the client's workloads from its previous cloud provider with security controls in place before production cutover.

The customer operated its production workloads with its previous provider without formally defined network trust boundaries, centralized security configuration management, or strong enforcement controls at the network and resource level. With workloads spread across shared network segments and no automated posture assessment tooling, security misconfigurations could go undetected, and traffic between application tiers was not constrained.
The previous deployment also lacked pod-level workload identity for Kubernetes workloads, relied on static secrets without centralized rotation, and used internet paths for access to cloud services. Left unaddressed, these gaps would have carried over to AWS, leaving the customer's production workloads with limited restrictions on traffic between tiers, long-lived credential risk, and internet-facing service paths from the moment of migration.
The customer engaged Aivar to design the target AWS architecture from the ground up, so that trust boundaries, secure system configuration, authenticated access, and policy-enforcement points were built in from the start rather than added after go-live.
Aivar built a custom event-driven remediation workflow that listens for credential risk findings from Amazon GuardDuty through Amazon EventBridge. A purpose-built AWS Lambda function disables the affected AWS Identity and Access Management (IAM) access key, tags the IAM user with incident metadata (timestamp, key ID, event ARN, and remediation status), and routes alerts to two Amazon Simple Notification Service (Amazon SNS) topics: one for credential exposure events, and a separate high-priority topic that integrates with on-call tooling and PagerDuty. The workflow adds a dual-severity escalation path and an audit trail stored in IAM user tags, so each credential event is both remediated and traceable.
Aivar designed and deployed an AWS CloudTrail → Amazon EventBridge → AWS Lambda → Amazon SNS alerting pipeline that monitors more than 30 Amazon Elastic Compute Cloud (Amazon EC2) network API calls across four categories: route tables, network access control lists (network ACLs), gateways, and Amazon Virtual Private Cloud (Amazon VPC) configuration. The AWS Lambda function formats AWS CloudTrail events into readable alerts, including actor, request parameters, and error codes, before delivery to the security team. It is paired with a weekly network ACL audit AWS Lambda function, triggered by an Amazon EventBridge scheduled rule (Monday 9 AM IST), that scans enabled Regions for unassociated custom network ACLs and delivers a structured report. This gives the security team real-time change alerting and a periodic review without third-party tooling.
Aivar built a custom incident response automation in which applying a SecurityStatus=Isolate tag to an Amazon EC2 instance, by a human responder or Amazon GuardDuty-integrated tooling, starts an isolation sequence. AWS CloudTrail captures the CreateTags API call, and Amazon EventBridge invokes an AWS Lambda function that replaces the instance's security groups with the Amazon VPC default security group (denying inbound and outbound traffic), disassociates the IAM instance profile to remove AWS API permissions, and optionally snapshots attached Amazon Elastic Block Store (Amazon EBS) volumes for investigation. A SkipRemediation=CloudSecurityAdmin tag provides a documented break-glass override, consistent across the remediation workflows in this engagement, so the security team keeps administrative control without disabling the automation.
Each production Region hosts an Amazon VPC with three-tier subnet isolation: public subnets for NAT gateways, private subnets for Amazon Elastic Kubernetes Service (Amazon EKS) workloads, and data-tier subnets for Amazon Relational Database Service (Amazon RDS) for PostgreSQL, Amazon ElastiCache (Redis OSS), Amazon OpenSearch Service, and Amazon DynamoDB. Data-tier resources have no public IP addresses and no internet gateway routes. Amazon VPC peering with controlled route tables provides cross-Region connectivity, and AWS Site-to-Site VPN provides the hybrid path to the previous cloud provider during migration.
Resources are defined in Terraform and stored in version control, and production changes are made through that code rather than the console. AWS Security Hub was enabled and reviewed before production cutover, with remediation of critical and high severity findings required as a go-live gate. Amazon Elastic Container Registry (Amazon ECR) repositories use scan-on-push, so findings of high or critical severity can be addressed before images reach Amazon EKS. Encryption at rest is enabled for data services including Amazon Simple Storage Service (Amazon S3), Amazon RDS, Amazon ElastiCache, Amazon DynamoDB, and Amazon EBS volumes.
AWS IAM Identity Center provides centralized console access protected by multi-factor authentication (MFA). Programmatic access uses temporary credentials issued by AWS Security Token Service (AWS STS) from IAM roles, with no long-lived IAM user access keys for human access. IAM roles for service accounts (IRSA) provide pod-level least privilege for Amazon EKS workloads, removing static credentials from Kubernetes manifests and environment variables. Secrets stored in the previous provider's key management service were migrated to AWS Secrets Manager with automatic rotation policies. Individuals access the AWS accounts with dedicated, uniquely attributable credentials, with activity recorded in AWS CloudTrail.
Amazon VPC endpoints (gateway endpoints for Amazon S3 and Amazon DynamoDB; interface endpoints for Amazon ECR, AWS Secrets Manager, and Amazon CloudWatch) are deployed in both Regions, keeping AWS service traffic on the AWS network instead of the internet. Security groups act as stateful enforcement points at the resource level and deny traffic that is not explicitly permitted. Network ACLs add a stateless enforcement layer at subnet boundaries, independent of security group rules. One NAT gateway per Amazon VPC serves as the controlled outbound internet path from private subnets. AWS Client VPN provides authenticated, encrypted developer access to private resources without exposing management interfaces to the internet.
KPI 1 — AWS Security Hub Critical and High Findings at Production Cutover
- Baseline: No AWS Security Hub or equivalent posture scoring existed in the source deployment; security findings were not tracked or measured before the engagement began.
- Target: No Critical or High severity AWS Security Hub findings at the Week 5 production cutover.
- Actual Result: No Critical or High findings confirmed before cutover sign-off; AWS Security Hub was enabled at the end of Week 2, leaving a two-week window for finding review and remediation before the Week 4 dry run.
- Measurement Methodology: AWS Security Hub findings view filtered by CRITICAL and HIGH severity; the count was confirmed as none by Aivar and Customer at both the Week 4 dry run gate and the Week 5 production cutover approval.
KPI 2 — Long-Lived Credentials Removed Across The Customer's AWS Accounts
- Baseline: 15 service credentials stored in the previous provider's key management service without automated rotation; human access to cloud resources through shared service accounts with no enforced MFA; no IAM credential baseline on AWS before the engagement.
- Target: No long-lived IAM user access keys for human access; secrets migrated to AWS Secrets Manager with rotation policies configured.
- Actual Result: No IAM user access keys present in the customer;s AWS accounts; secrets from the previous provider migrated to AWS Secrets Manager with automatic rotation configured per secret type.
- Measurement Methodology: IAM credential report confirming no access keys; AWS Secrets Manager console listing with rotation status confirmed active; validated at the Week 5 production cutover and recorded in the migration closure report.
1. AWS DMSReplication Lag Risk: AWS Database Migration Service (AWS DMS) change datacapture (CDC) replication lag spikes, caused by write volume on the sourcePostgreSQL database, were identified as a high-likelihood risk. Mitigationincluded sizing the AWS DMS replication instance with headroom, monitoring lagcontinuously through Amazon CloudWatch, and requiring replication lag of 0sustained for one hour as a cutover gate. This has been adopted as a standardmethodology element for future migrations to AWS.
2. VPN Bandwidth for Large Storage Transfers: AWSSite-to-Site VPN bandwidth constraints for large object storage transfers toAmazon S3 were addressed by scheduling bulk sync during off-peak hours, tuningthe parallel thread count of the transfer tool, and enabling Amazon S3 TransferAcceleration. Bandwidth assessment during discovery is now a standard stepbefore committing to migration schedules.
Aivar conducted a total cost of ownership (TCO) analysis for the dual-Region architecture: right-sizing Amazon EKS node groups, Amazon RDS instance classes, and Amazon ElastiCache nodes to the Customer's live traffic patterns, and moving on-demand compute and database spend to committed-use pricing through Compute Savings Plans (an AWS Savings Plans option) and Amazon RDS Reserved Instances, targeting a 30–40% cost reduction versus on-demand pricing once post-cutover traffic patterns stabilize. Estimated AWS annual recurring revenue (ARR) is approximately USD 473,679 per year based on the deployed footprint across two production Regions.
Incorporate AWS DMS lag monitoring thresholds, bandwidth assessment during discovery, and mandatory cutover dry runs as standard methodology elements for future migrations to AWS.
Deliver Compute Savings Plans and Amazon RDS Reserved Instance recommendations with a target of 30–40% cost savings versus on-demand pricing for migration customers after post-cutover stabilization.
Introduce mandatory post-cutover performance tuning checkpoints at 30, 60, and 90 days, covering Amazon EKS node sizing, Amazon RDS instance class, and Amazon ElastiCache node right-sizing based on live traffic patterns.